
Identify a correlation rule to distinguish the most significant alert from a given set of events from multiple data sources...
Identify a correlation rule to distinguish the most significant alert from a given set of events from multiple data sources...
Map DNS logs and HTTP logs together to find a threat actor Implementing Cisco Cybersecurity Operations (210-255) Map DNS, HTTP,...
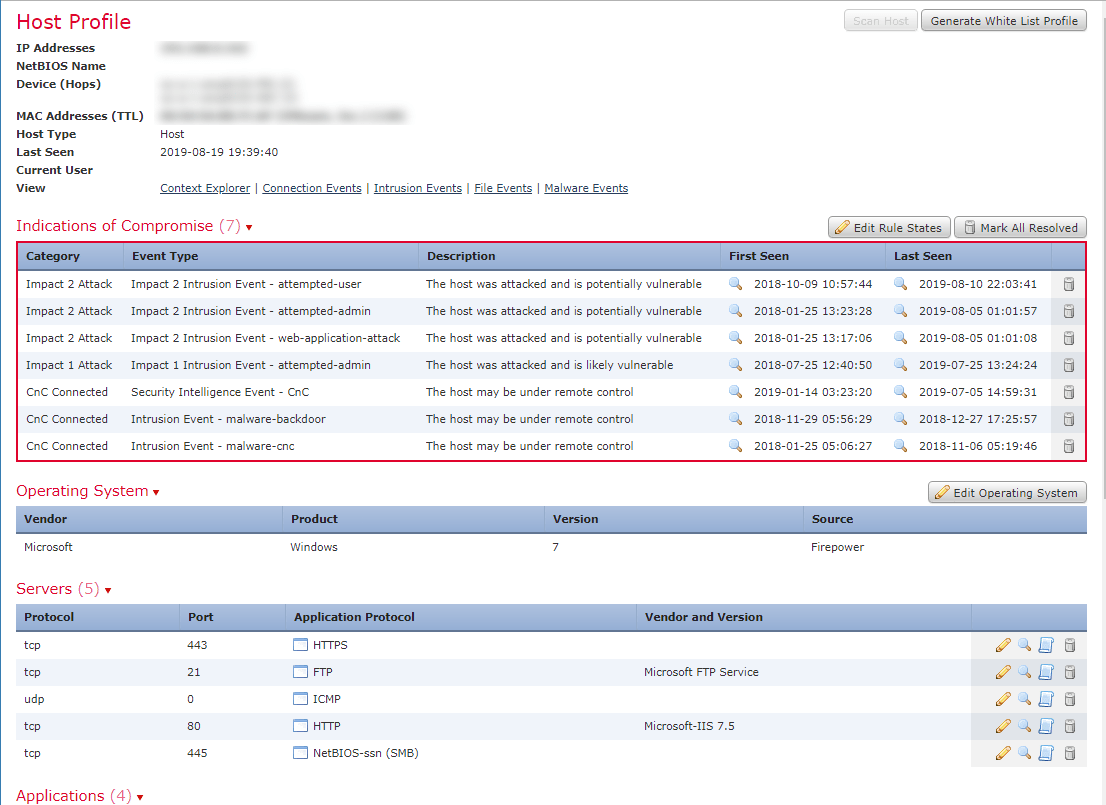
Identify potentially compromised hosts within the network based on a threat analysis report containing malicious IP address or domains Implementing...
Rackstuds are one of those things that you didn’t know you needed until you first get some. Cage nuts have...